Mobile Security: Checklists for Testing Attack Surfaces to Protect Your Phone
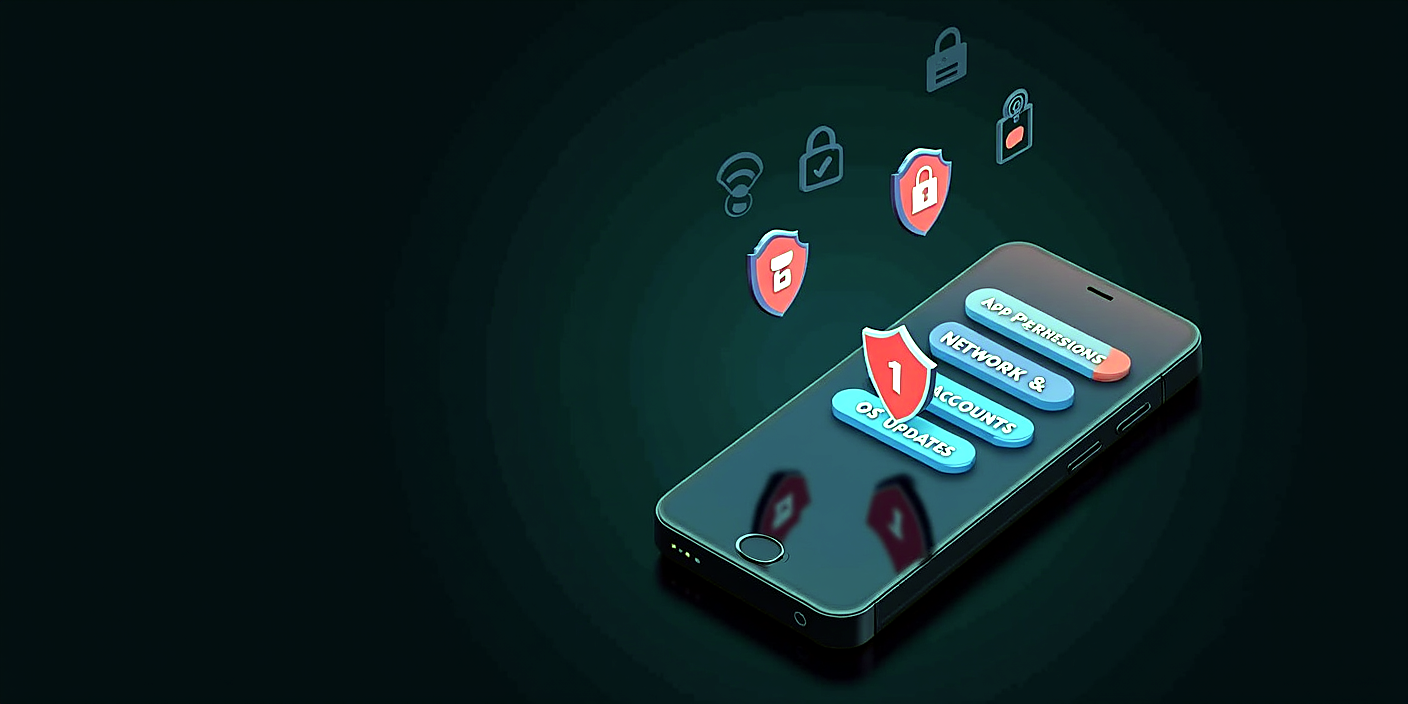
Identify mobile security threats: app permissions, network and account vulnerabilities, check for OS updates to securely protect your phone.
Distinguishing incoming threats and "attack surfaces"
To improve mobile security, first you need to identify which channels your phone is vulnerable through. Usually, threats are concentrated in several directions: app permissions, network connections, browsers/downloads, and accounts (SMS, password, authentication).
The following checklist will clearly tell you where to start: which apps request permissions, which network you're connecting via, and which accounts (Google, Apple ID, social media) are unprotected.
- Apps: permissions (camera, location, contacts), background activity, "overlay" (requesting permission from above) features.
- Network: Wi-Fi, VPN, mobile network access, browser downloads.
- Accounts: password strength, SMS dependency, verification methods, device list.
- Operating system: delayed updates, presence of security patches for browser and system components.
Updating the operating system and apps: precise mechanism and verification
The purpose of updates is to install fixes (patches) for numerous vulnerabilities. If your phone's OS (Android or iOS) and important apps are delayed in receiving security patches, the risk of exploitation through old vulnerabilities increases.
To check: see if there are system updates available, which browser version you're using, and whether banking and authentication apps are up to date. Putting this into place is considered one of the most beneficial steps for security because many attacks target devices that remain on older versions even after patches have been released.
- Android: "Settings" → "System" → "System updates".
- iOS: "Settings" → "General" → "Software Update".
- Apps: Check the "Updates" section within the App Store.
Passwords and authentication: protecting recovery channels as well
The most commonly breached area in mobile security is not the password itself, but the account recovery methods. For example, if recovery is done via SMS, it may be possible to steal access through SIM-swapping or by identifying the phone number.
Therefore, when setting up authentication, check three things: password strength, recovery method (preferably an app or hardware token instead of SMS), and device list (which devices are linked to your account).
- Go to the "Login" or "Security" section in your account settings.
- Turn off Two-step verification (2FA). If possible, choose a code based on an app or hardware key.
- In the Devices section, remove any devices you do not recognize.
- In the Recovery section, reduce SMS dependency: generate backup codes and store them securely.
Network security: Check Wi-Fi, browser, and HTTPS
The most common problem when your phone is connected to a network is connecting to untrusted or fake networks. In this case, malicious pages may ask for login information or redirect downloads to harmful files.
Browsers and systems should use HTTPS because it encrypts connections. A specific signal you can check: the address bar shows "https" and no certificate errors appear.
- When selecting a Wi-Fi network:
- Be cautious of networks with similar names such as “free-wifi”/“hotel-wifi”.
- Use networks that do not require passwords to the minimum extent possible.
- In your browser:
- Do not enter login details on pages with certificate errors.
- Carefully review file download permission requests.
WORKING MECHANISM: How permissions control and "least privilege" work
In Android and iOS, apps access resources by requesting permissions. The essence of this model is granting an app only the necessary permissions (least privilege). As a result, malicious code in an app cannot have full access to all data.
For example, if a camera app is granted permission to operate only when taking pictures, the possibility that it can activate the camera unnoticed in background mode decreases. Similarly, setting location permissions to "only while the app is active" limits background monitoring.
- Check Permissions: Settings → Apps → (required app) → Permissions.
- Limited Permission Level: Instead of “Always,” choose “Only when the app is in use.”
- Limit background activity: Disable background mode restrictions in battery/usage sections if your system allows it.
- Overlay and special permissions: Only grant these to necessary apps.
HISTORY: How mobile security practices have evolved mobile security
Security approaches for mobile devices have changed over time. Previously, the main focus was on antivirus-like methods, but later internal system mechanisms (permission models, encryption, app store control) became more dominant.
Below is a brief chronology of the security practices direction:
- Early 2010s: As smartphones became widespread and apps started spreading from stores, the concept of permissions and app isolation gained strength.
- 2012–2016: Device-level encryption and more precise permission management practices expanded; users had greater ability to control permissions.
- 2018: Increased attention was given to mobile networks and browsers TLS, enhancing protection against intrusive methods such as man-in-the-middle (MITM) attacks.
- 2020–present: The direction became more focused on "supply chain" (apps and libraries chain), misconfiguration, and social engineering (e.g., phishing pages).
PRACTICAL CONFIGURATIONS: A specific checklist to protect your phone
The following practical steps give you a verifiable result without empty promises. Each item has places where it can be performed and they often complement each other.
Work in the following order: first device security, then account, followed by app permissions and network.
- Disable screen lock: Remove PIN/Password and use a more complex method if possible.
- Cautiously configure biometrics: Do not set the password to "rarely used" mode, instead ensure you have the ability to activate it; do not avoid entering your password when requested by the system.
- Disable 2FA: Enable two-factor authentication for Google/Apple ID and important accounts.
- Check permissions: Minimize camera, microphone, location, contacts, and "overlay" permissions.
- Update apps: Always keep banking, authentication, and browser apps updated.
- Remove unknown devices: Check for connected devices in the account security section.
Typical errors: relying only on SMS to verify, leaving permissions "always" enabled, and entering login credentials on pages with certificate warnings. These three points often recur repeatedly.
CORRELATION: How does a permission model differ from a security approach?
Permissions and isolation are present in both platforms, but the practical control interface and types of permissions may look different. The following table helps you quickly determine "where to focus."
| Direction | Android | iOS |
|---|---|---|
| Location permission | Variants such as "While in use" are available | Variants such as "When the app is being used" are available |
| Camera/microphone | Per-app settings and background restrictions | Permission control per app and during use |
| Special permissions | For example, "overlay" and entry options are in separate sections | Special permissions are usually shown in special settings |
| 2FA | Set up via code inside the app or authentication apps | Authentication apps, backup codes and security settings |
FAQ
Can I use only fingerprint on my phone instead of a password?
Fingerprint is usually convenient but it's not recommended to be limited "only" by that: there are situations where the system will ask for a password (reboot, long inactivity, some security policies). Therefore, have a PIN/password ready and make sure your security settings are adjusted accordingly.
Does connecting to Wi-Fi via VPN automatically increase safety?
VPN encrypts traffic but doesn't eliminate all risks. For example, if a malicious app forces you to open a phishing page, the VPN still won’t completely prevent access to harmful content. Therefore, in addition to using a VPN, browser warnings and checking permissions are also necessary.
Are app permissions "If it asks, then it's needed" true?
No. Permissions aren't always required. Even if an app function requires it, restrict the permission as much as possible: location only while the app is active, give overlay permission only when absolutely necessary, turn on camera/microphone only during use — such restrictions are beneficial.
Where do malicious apps most commonly come from?
In many cases they spread through unofficial installations (via downloaded files) and phishing links that trick users. Therefore, it's important to disable installation from unknown sources and check the source of any file being downloaded.
How can I quickly detect if my account has been compromised?
Rapid signal: suspicious changes in login location or time, unfamiliar devices on your list, or "login" activity notifications. Check connected devices in security settings and reconfigure verification codes/2FA methods.
If my phone is lost, what should I do first to protect myself?
First, enable/disable the ability to find and block devices remotely (the "find" service depends on the platform). Then revoke sessions in accounts and recheck 2FA recovery methods. If you are concerned about SIM swapping, it is also useful to ask your mobile operator about number protection policies.
Conclusion
Mobility security is not just turning on a single setting, but combining several specific control points: system updates, 2FA and recovery channels in the account, minimizing app permissions, and inspection habits on network and browser.
To achieve the best results, follow the checklist sequentially: first set up device updates and screen lock settings, then strengthen account security, next minimize permissions, and finally apply precautions on the network.